
NanoClaw
A small assistant that runs each agent in its own Linux container and keeps credentials outside it.
Instead of Hosted AI assistants and agents
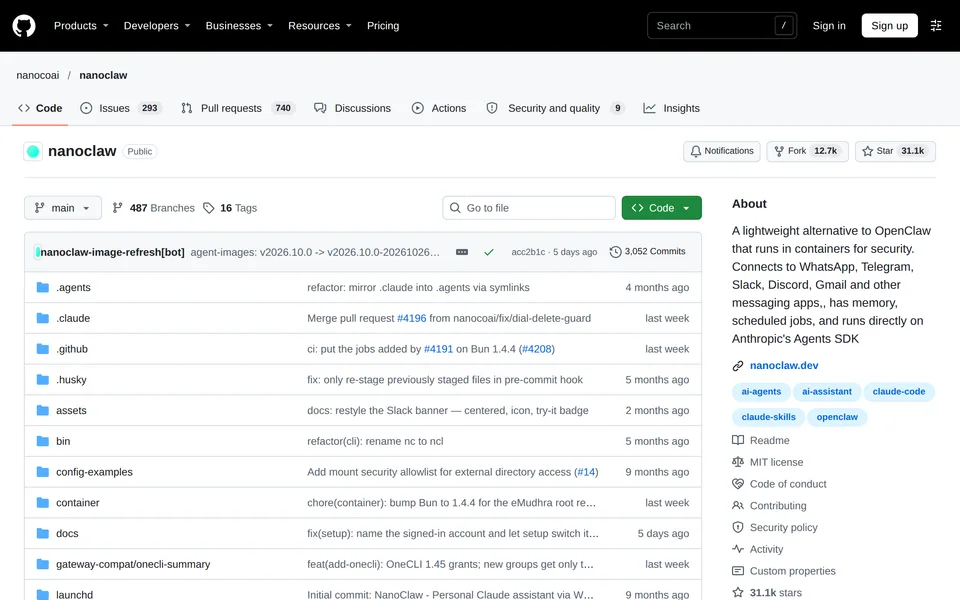
Screenshot from github.com/qwibitai/nanoclaw, taken 2026-10-30, shown to help you recognise the tool. It belongs to its maker. Ask us to remove it.
Giving an assistant your logins has the energy of handing a stranger your house keys, and NanoClaw answers by putting each agent in a container that can only see what you mount. The README says credentials stay outside the container, with a gateway injecting them into outbound requests, and it contrasts that with OpenClaw's application-level allowlists in a single Node process.
NanoClaw scores a 4 on lock-in and delivery and a 3 on footprint, self-direction, power and longevity.
The code is MIT licensed under the nanocoai organization, and the README is written in the first person without naming an author. By default it uses Claude Code through Anthropic's Agent SDK, and other providers, including local models through Ollama, are add-on skills. Setup needs Docker and Node, and fetching the prebuilt image needs a free account, so the maintainers see your email address and when you ask for an image. It also reports anonymous setup diagnostics, and NANOCLAW_NO_DIAGNOSTICS=1 turns them off.
- Runs each agent in a Linux container with credentials kept outside it
- MIT licensed, with Claude Code as the default and local models as an add-on
- Anonymous setup diagnostics, and a free account for the prebuilt image
What stands out
Do you make NanoClaw? Get the badge for your site
This badge reports a dated review. It is not a certification and it costs nothing. Link it to this page and leave the numbers alone: the image always shows the current score.
For dark backgrounds, use nanoclaw-dark.svg in place of nanoclaw-light.svg.
Other tools for “get an assistant that works for me”
 nanobotA small self-hosted Python assistant that works through a web page, a terminal or your chat apps.
 IronClawA Rust assistant that runs untrusted tools in WebAssembly sandboxes and says it collects no telemetry.
 MoltisA single Rust program that runs a persistent assistant on your own hardware, with every command sandboxed.
 OpenClawAn open-source AI assistant that runs on your own computer and works through your chat apps.
 Hermes AgentAn open-source AI agent that learns skills from the tasks it does and remembers you.